Outside. Inside. Microsoft 365.Checked, not guessed
We find what an attacker can reach: on the internet, on your office network and in Microsoft 365. Then we take the serious findings back to the target, test them live and hand you the proof. You fix what is real.
Hosted in Sweden.Platform, database and backups.
Six problemsWe go after every one
Six things we hear again and again. Every answer below runs in PollySec today.
Account takeover and fake invoices
“Someone got into our email and sent a fake invoice.”
Close the doors fake invoices come through.
How We check SPF, DKIM and DMARC so nobody can send mail in your name, and whether your staff's passwords are already out there. In Microsoft 365 and Entra ID we check that MFA covers everyone, that legacy authentication is blocked and that no inbox rule quietly forwards mail outside the company.
See how we check thisThe forgotten server
“We didn't know that was still online.”
See everything you have on the internet, including what you forgot.
How We keep mapping your domains and subdomains all year, test every open service, and put vulnerabilities in the CISA Known Exploited Vulnerabilities (KEV) catalog and exposed remote access at the top of the list.
See how we check thisPasswords already out there
“An employee's password had leaked months ago.”
Know which accounts to reset before someone uses them.
How We check the addresses we can find for your domain against breaches and infostealer logs, and rank stolen logins above almost everything else.
See how we check this- In the larger packages
The office network nobody looks at
“We have no idea what is actually on our office network.”
Every device on your network, its weaknesses, and a trap for anyone who shouldn't be there.
How A small sensor maps the devices on your internal network and tests what they expose, with a profile of its own for production equipment. In the full package, decoys raise the alarm the moment someone touches them.
See how we check this 400 findings and no time
“The scanner gave us 400 findings.”
A short list of what is real, in the order that matters.
How ARIA tests serious findings and clears the false ones, with the evidence. One finding per installed software version, listing every CVE that applies. Wrong findings are withdrawn and never count as fixed.
See how we check this“Show us you're secure”
“Our customer wants proof for NIS2.”
Evidence ready when the customer, auditor or insurer asks.
How NIS2 and ISO 27001 evidence reports, a remediation plan, and a trust link you can send to a customer instead of filling in another questionnaire.
See the NIS2 evidence
The numbers behind the problems
- 31%of breaches started with an exploited vulnerability, now the most common way in.Verizon DBIR 2026
- $3.04bnlost to business email compromise in 2025, in complaints to the FBI.FBI IC3 Internet Crime Report 2025
- >44%of cyber incident reports in Sweden in 2025 concerned an incident that began at a supplier.NCSC annual report 2025
Three ways inOne list to fix
We go where an attacker goes, test what is serious, and hand you one list with the worst first. If you run a Continuous Threat Exposure Management (CTEM) programme, this is its discovery, prioritisation and validation, running all year.
01
Outside
Nothing to install
We map your domains and subdomains from our cloud, test the services they expose, and keep looking, all year.
02
Inside
One small sensor per site
It maps and tests the devices on the networks you assign, with a profile of its own for production equipment.
In the larger packages
03
Microsoft 365
One consent, a few clicks
We check the settings that decide who can sign in and where your mail goes. Every day.
ARIA
ARIA checks
Serious findings, tested
ARIA takes serious findings back to the target with real tools and shows what came back. Wrong findings are withdrawn.
✓
You fix, we re-test
One list, in order
One risk score from 0 to 100 weighs severity, CVSS, EPSS and the CISA KEV catalog, so the worst comes first. Fixed something? Re-test that one finding.
Scanners guessARIA checks
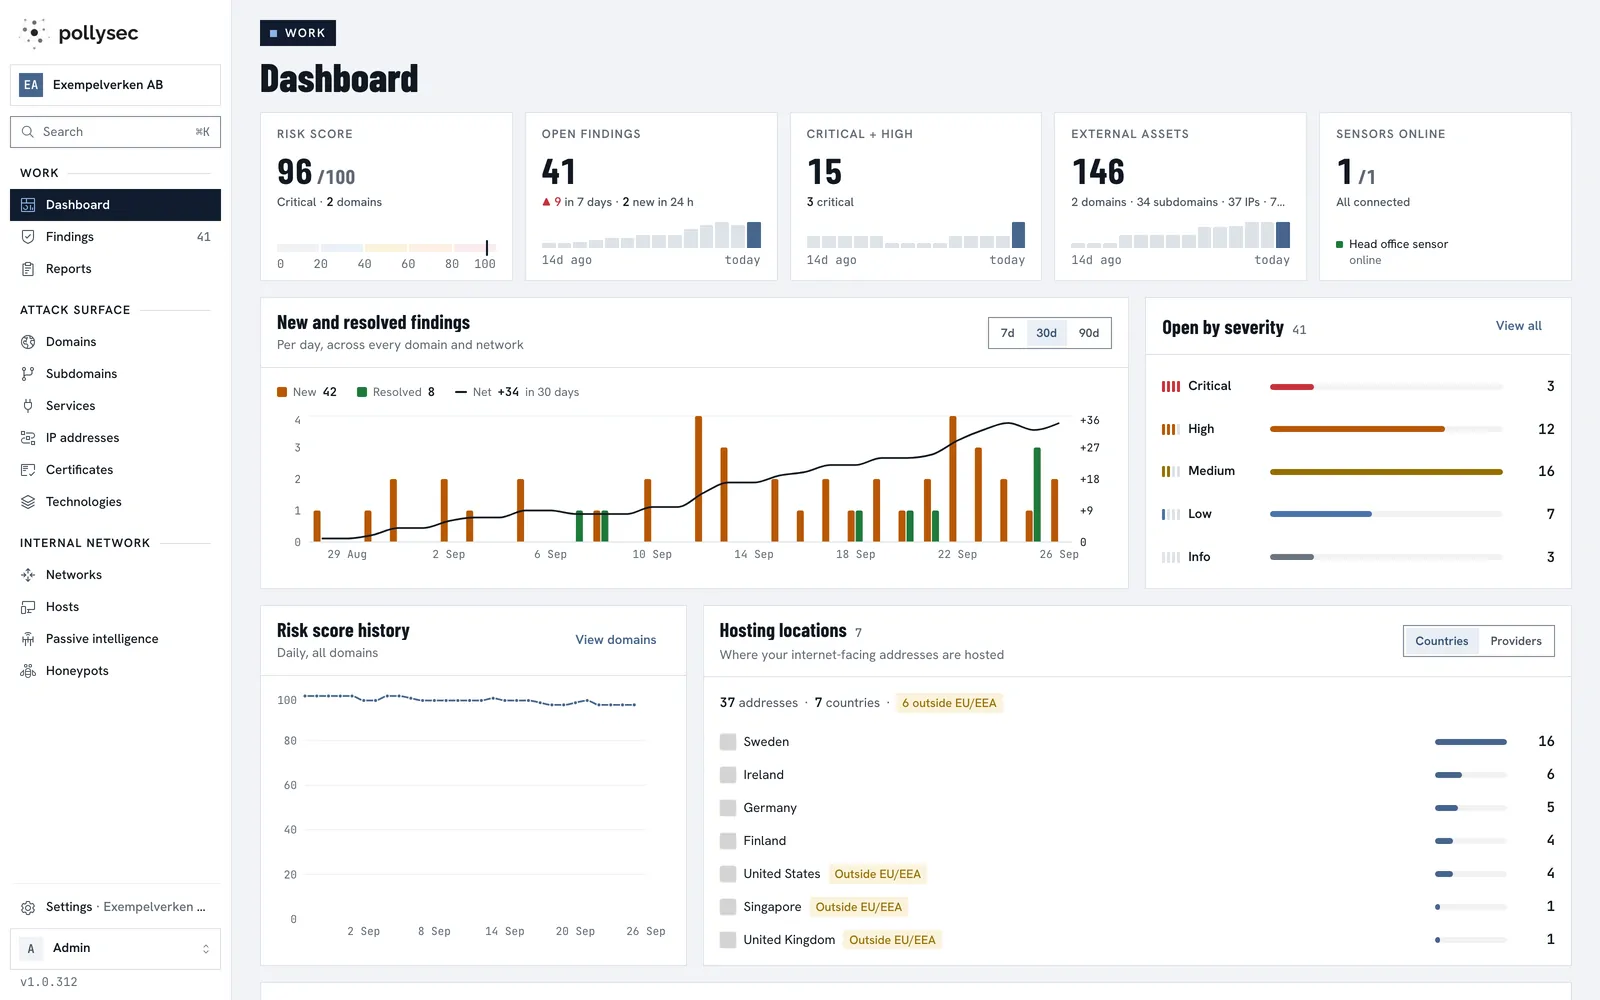
When we find something serious, ARIA goes back to the target with real tools and shows you what it saw. Real? You get the proof. False? It is closed with the reason, after a second review. Findings a test cannot settle are marked as such.
- Real tools against the live target, picked per finding
- Every quote must match what the test actually returned
- Closing a false positive takes a second review
- Wrong findings are withdrawn, never counted as fixed
Your Microsoft 365 is where the money movesWe check the locks
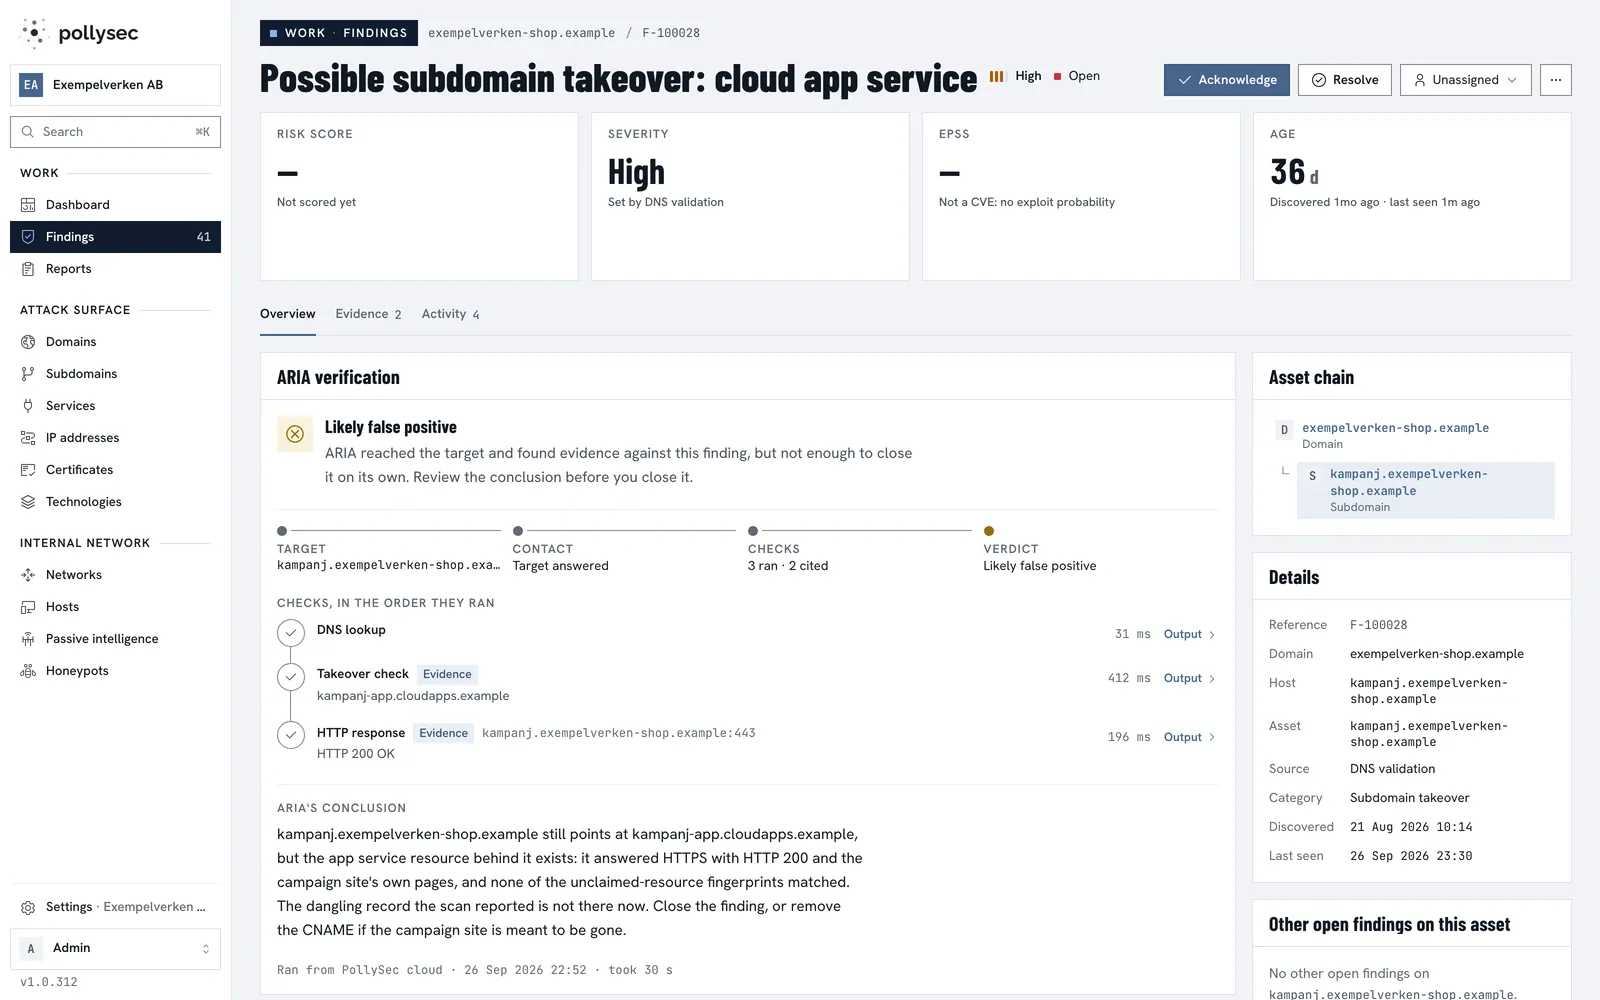
We scan your Microsoft 365 tenant and Entra ID for vulnerabilities and misconfigurations, every day: 37 checks across sign-in and MFA, admins and guests, apps, mail and files. Fake invoices start with a taken-over mailbox, and these are the settings that stop it.
What we catch
- MFA not required for everyone
- Admins with no MFA registered
- Legacy authentication that bypasses MFA
- Too many Global Administrators
- Admin accounts synced from on-premises AD
- Guests holding directory roles
- Apps with more access than they need
- Inbox rules forwarding mail outside the company
One consent from your admin. Checked every day.
Check your Microsoft 365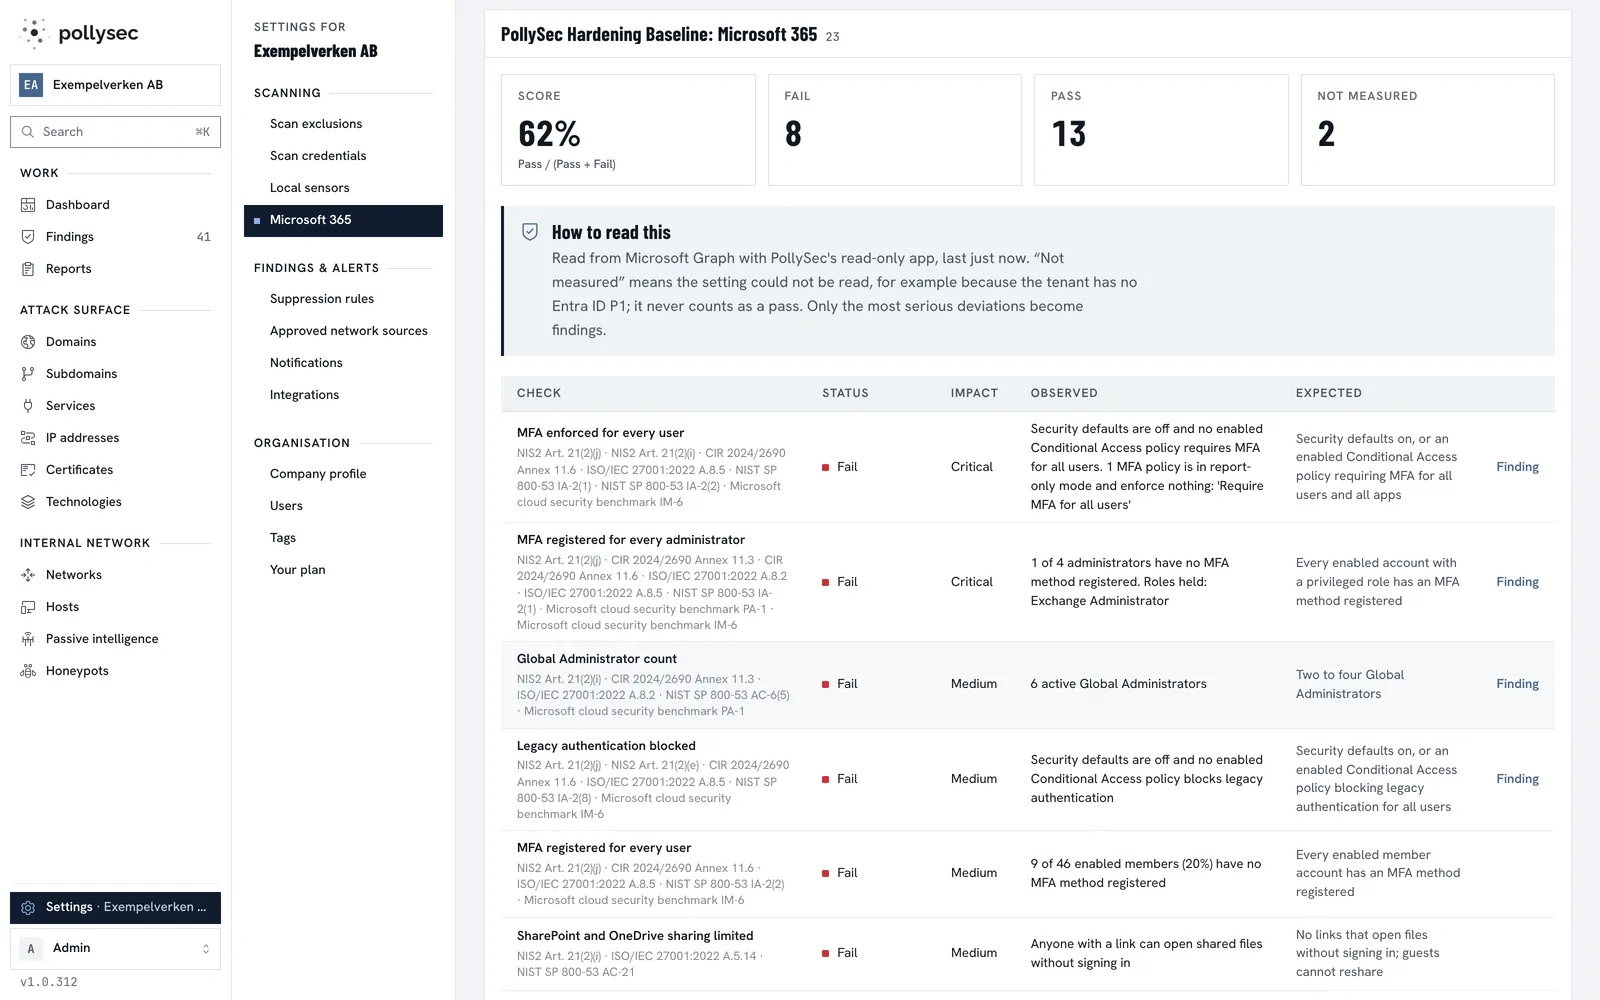
Built the way attackers thinkProven the way auditors want
Three surfaces, one platform
Attackers don't care which tool you bought. We look where they look: the internet, your office network and Microsoft 365.
AI that checks its own work
ARIA tests serious findings live against the target and must quote what the test returned. Your team's time goes to what is real.
We withdraw our own mistakes
A finding that turns out wrong leaves your history. It is never counted as fixed, so your numbers aren't padded with our errors.
Traps as well as scans
Scans find weaknesses. Decoys on your network catch someone who is already inside.
Built for real networks
Printers, production lines and old equipment get a profile of their own. The sensor works on the networks you assign, and only there.
Compliance as a by-product
NIS2 and ISO 27001 evidence falls out of the work you already do. No separate project for the auditor.
Made for IT partners
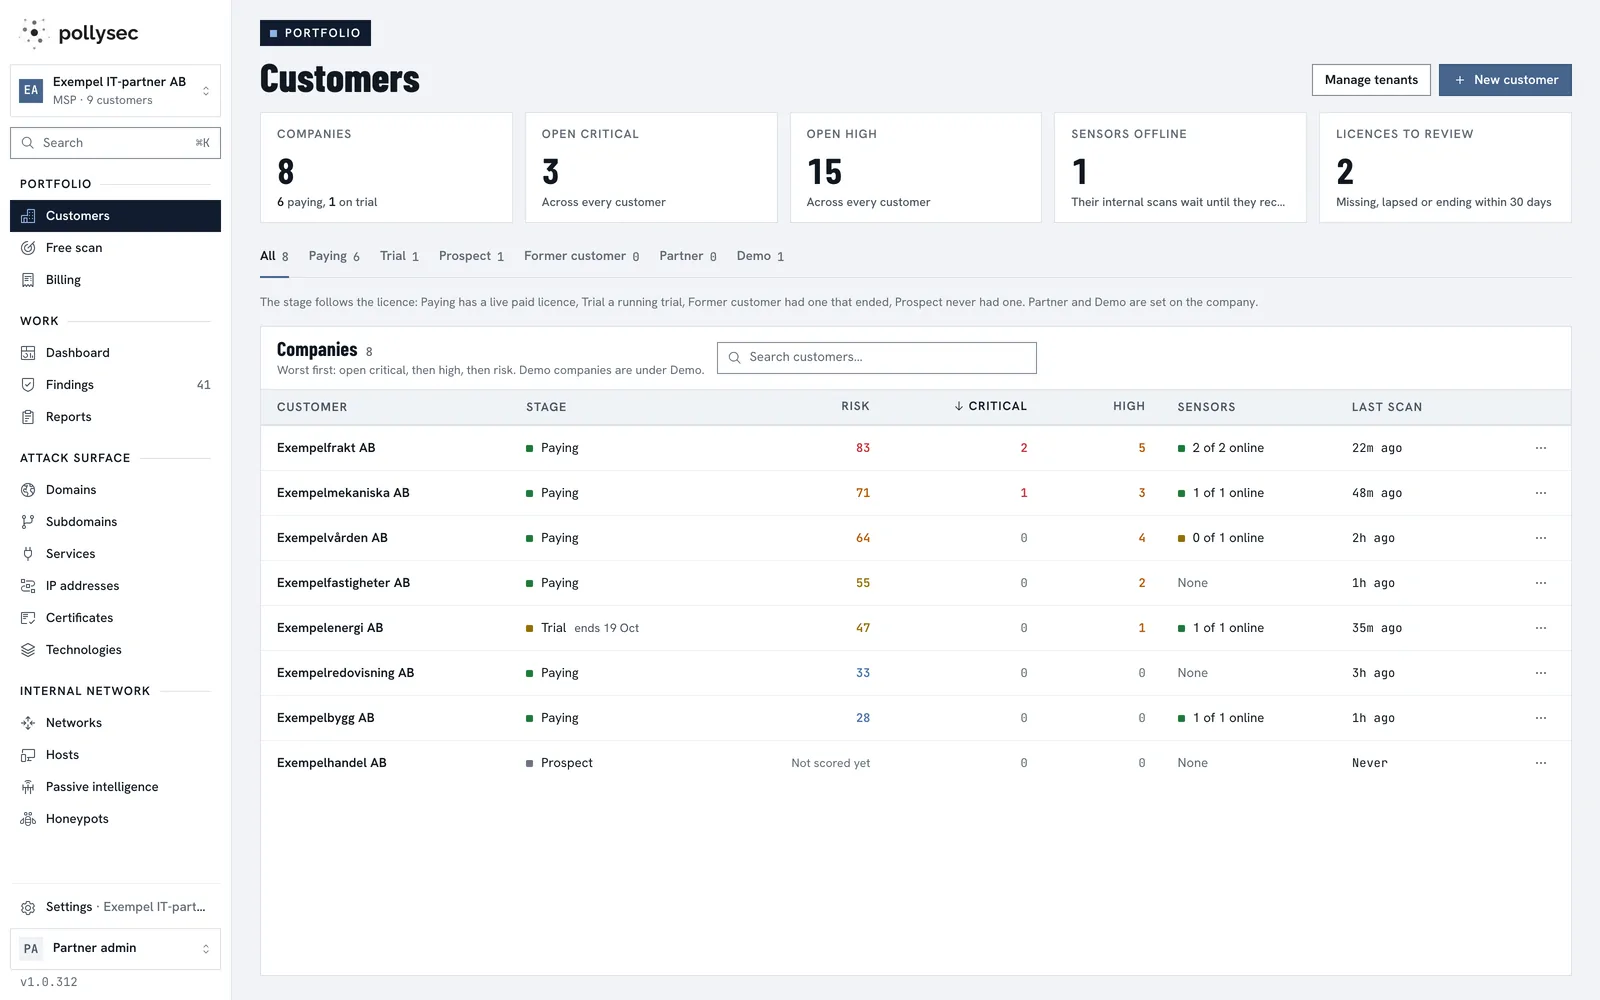
Every customer in one console, a portfolio view and partner billing, so your partner can deliver it to many customers.
Hosted in Sweden
Platform, database and backups run in Sweden, by a Swedish company.
Why one platform beatsthree tools and a yearly test
Your pen tester covers one week. We cover the other fifty-one.
A pen test is worth the money. It is also a deep look at one moment, and the rest of the year the door stays ajar.
| PollySec | Typicalvulnerability scanner | Typicalattack-surface tool | Typicalyearly pen test | |
|---|---|---|---|---|
| Where it looks | ||||
| Your internet-facing systems, forgotten ones too | Yes: Finds them itself | Partly: The list you give it | Yes | Partly: Agreed scope |
| Your internal network | Yes: One sensor per site | Yes: Often | No: Usually not | Partly: If in scope |
| Microsoft 365 and Entra ID: vulnerabilities and misconfigurations | Yes: 37 checks, every day | Partly: Sometimes, as an add-on | No: Usually not | Partly: If in scope |
| How often it looks | Yes: Every day or week | Partly: On a schedule | Yes: Ongoing | No: Once or twice a year |
| What reaches you | ||||
| Serious findings tested live, with evidence | Yes: ARIA, automatically | No: Usually not | Partly: Sometimes | Yes: By hand |
| False positives cleared, with the reason | Yes: After a second review | No: Rarely | Partly: Sometimes | Yes |
| Wrong findings withdrawn from your history | Yes: Never counted as fixed | No: Rarely | No: Rarely | Not applicable |
| Beyond scanning | ||||
| Decoys that catch someone already inside | Yes: Seven decoys, one click | No: Usually not | No: Usually not | No |
| Listens for spoofing and rogue devices | Yes: Around the clock | No: Usually not | No: Usually not | Partly: During the test |
| Proof and delivery | ||||
| NIS2 and ISO 27001 evidence | Yes: Reports and a trust link | Partly: Sometimes | Partly: Sometimes | Partly: One report per test |
| Built for IT partners: many customers, partner billing | Yes: Portfolio and billing | Partly: Varies | Partly: Varies | Not applicable |
| Hosted in Sweden | Yes: Platform, database, backups | Partly: Varies | Partly: Varies | Not applicable |
| Where a pen test wins | ||||
| Deep manual testing by a human expert | No: Keep your pen test for that | No | No | Yes: That is the point |
Typical is what each category is generally built to do, as we assessed it in September 2026. Individual products vary. The internal network comes with every package but the smallest, decoys with the full package.
One platforminstead of a stack of tools
We don't publish prices. They are set with you or your IT partner. ARIA verification, the compliance reports and the internal network come with every package but the smallest, decoys with the full package.
Ask what it costs for you- One platform instead of a scanner, an attack-surface tool, a Microsoft 365 audit and a pile of spreadsheets.
- No hardware to buy to get started: for a pilot, we lend you the sensor.
- Delivered by your IT partner, as part of the service you already pay for.
- Checked findings instead of noise to sort.
- Evidence for NIS2 and ISO 27001 without a separate project.
- Start with the outside, add the inside and Microsoft 365 when you're ready.
Built for the partnerswho look after Swedish businesses
Turn “we should do more security” into a service you can sell next week, without hiring analysts to sort noise.
- One console for every customer
- A portfolio view across all of them
- Partner billing, direct to the customer or through you
- A demo company for sales meetings
- Verified findings, so you don't need a triage team
Fair questions
Do we have to install agents on every computer?
No. The outside and Microsoft 365 need nothing installed. For the inside you place one small sensor per site; it scans the network from there, with no software on your computers. For a pilot we lend you the sensor.
Can our network take it?
Yes. Every network gets the profile it needs, from full depth to a profile of its own for production lines, and printers and industrial equipment get special handling. The sensor works on the networks you assign, and only there.
What can you access in our Microsoft 365?
The settings behind our checks: sign-in and MFA, admin roles, guests, app permissions and file sharing, plus inbox rules if you allow it. Your admin approves it in Microsoft's own consent screen, and you disconnect whenever you like.
Where is our data?
The platform, database and backups are hosted in Sweden. Some analysis, such as AI verification and breach lookups, uses carefully chosen services outside Sweden. E-mail addresses are removed before anything reaches the AI model.
Can we trust AI with security decisions?
ARIA doesn't guess. It runs a small set of tests within strict time and tool limits, and must quote what the tests actually returned. Closing something as a false positive takes a second review. It never touches industrial networks, and you can always overrule it.
We already have a pen test, antivirus and an IT partner.
Good. Keep them. A pen test is a deep look at one moment. We watch every day in between. Antivirus protects each computer. We go after what is exposed around them. And your IT partner can run PollySec for you.
Type your domain.See what they see
DNS, email spoofing, TLS and your web stack, checked from our cloud. No signup. One scan a day, so pick the domain that matters.
# PollySec · one free scan per visitor
# type a domain below and press Enter
e.g. example.se. We don’t keep the result.
30 minutes.Your findings. Our screen
We map your surface live, let ARIA test what it finds, and show you exactly what to fix first. If it fits, you get a 30-day pilot with a loaned sensor.
Rather email? hello@pollysec.com
Booked
A person replies within one business day, from hello@pollysec.com.